HAR files hold cookies, auth headers and full response bodies. Most viewers either upload them or render captured pages that happily load their trackers again. HAR Explorer is a single index.html plus a Linux launcher, built so that opening a capture, including rendering its HTML pages, cannot send any of that anywhere.
har-explorer
Offline viewer for HTTP Archive (.har) captures.
Open a HAR file without letting it phone home.
WebWeb app, CLIHTML, JavaScript, Shell, bubblewrapMIT
Why it exists
How it works
Two layers. The launcher runs the browser under bwrap with a private network namespace holding only a downed loopback device, a read-only filesystem and an empty /run, so no local daemon (systemd-resolved, D-Bus, nscd) can resolve names or connect on its behalf. It checks from inside the sandbox that only lo exists and refuses to start otherwise. The browser gets a throwaway profile; "Save body" can only write to $XDG_DOWNLOAD_DIR.
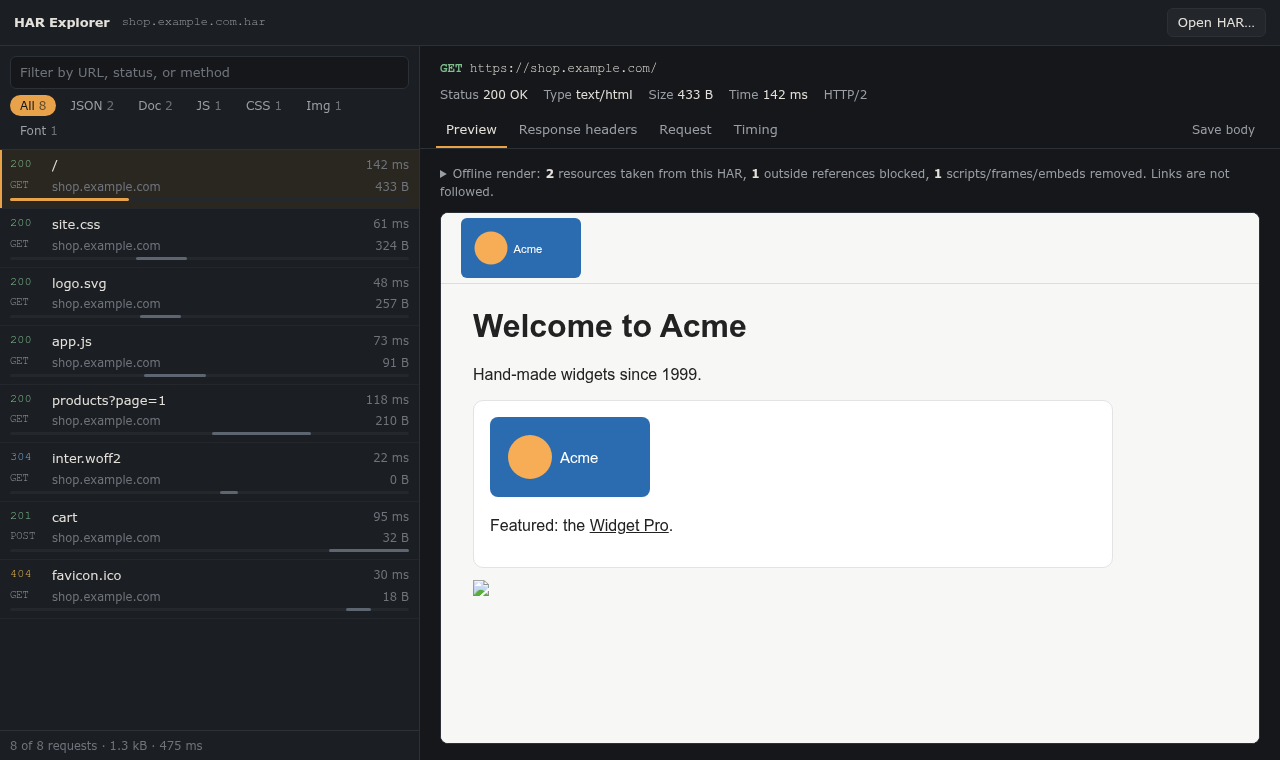
The page itself sets a Content-Security-Policy allowing only inline code and data:/blob: URLs, so every http(s) request is refused. HTML previews are parsed inertly, stripped of scripts, frames, embeds and event handlers, get their subresources swapped for data: URLs from the same HAR, and render in a sandboxed iframe with its own CSP. Links are shown but cannot be followed.
Limits, stated plainly: /dev/dri is passed through when present, and the sandbox can still talk to your display server. On X11 that makes the browser an ordinary X client of your session.
What it does
- Request timeline with a waterfall; filter by URL, status prefix, method or type.
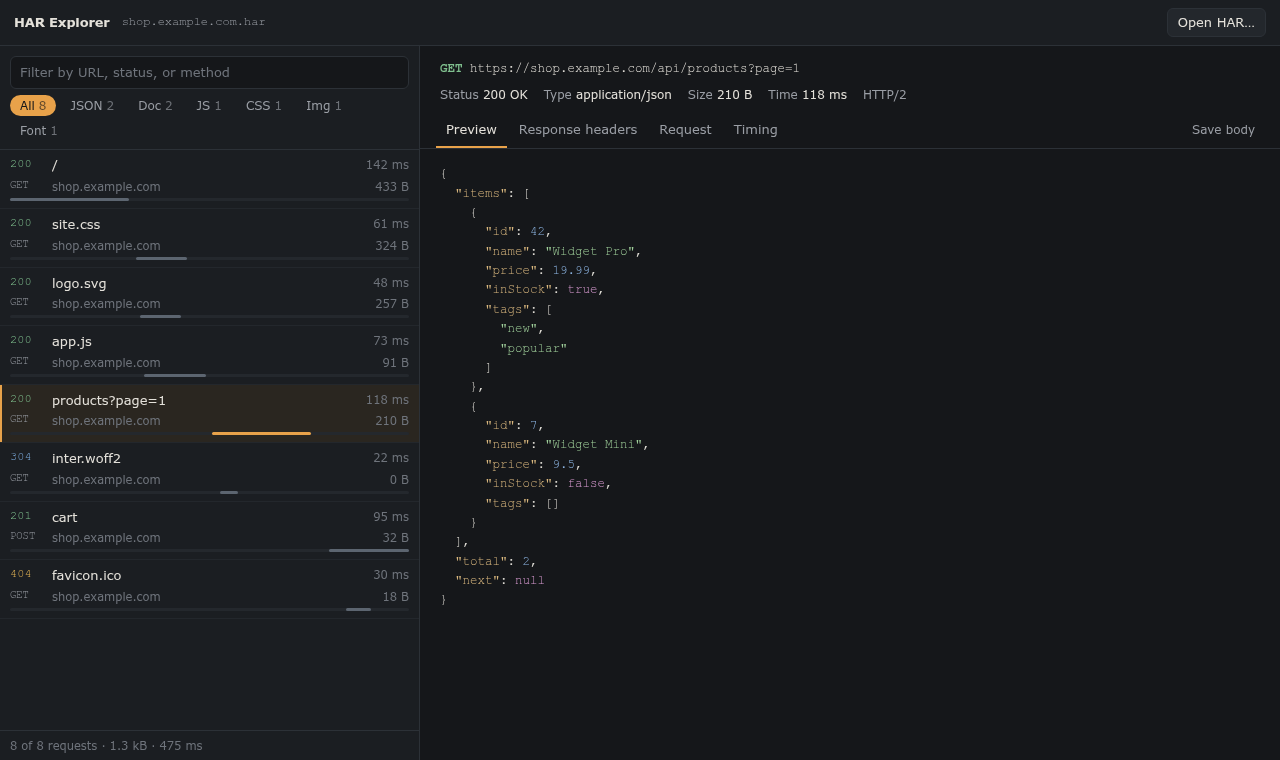
- Previews: highlighted JSON, images, audio/video, text, and offline-rendered HTML.
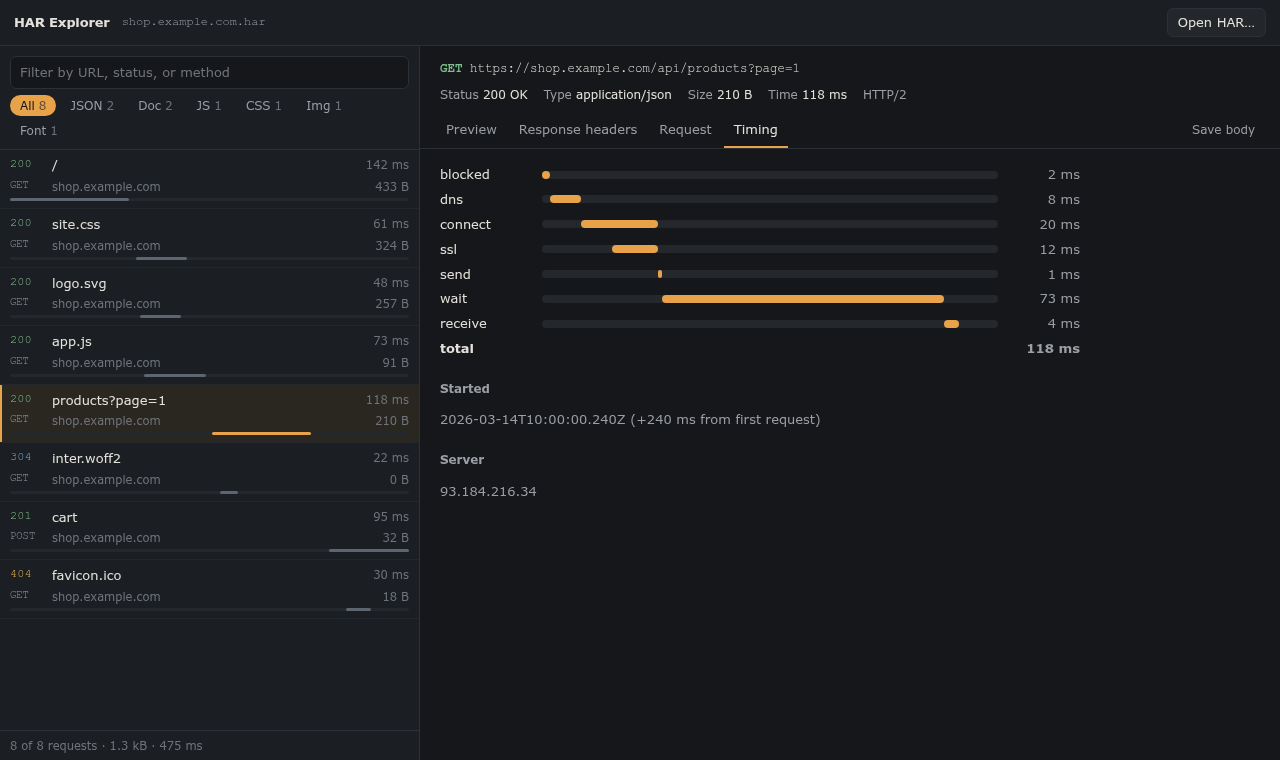
- Headers, query string, cookies, POST bodies and per-phase timings.
- Keyboard:
j/k,/to filter,1–4for tabs.
Use
./har-explorer capture.har
./har-explorer          # empty viewer, drop a file on it
Needs bubblewrap with unprivileged user namespaces and Chromium, Chrome or Firefox (HAR_EXPLORER_BROWSER overrides). Without the launcher, open index.html in any browser; then only the CSP layer protects you.
-
A JSON response, highlighted. -
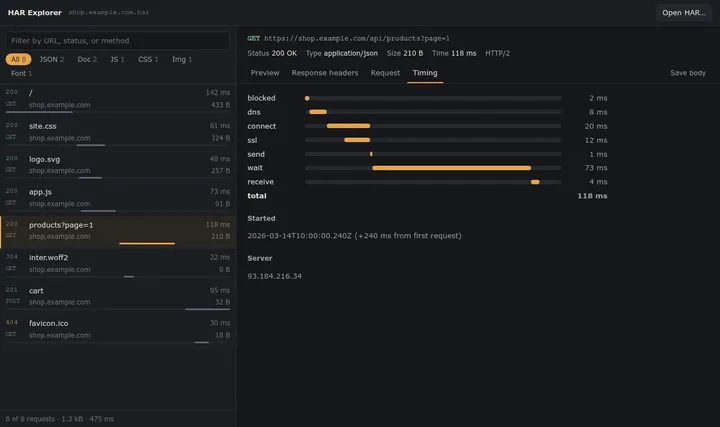
Per-phase timings for one request.